Loading JobOrbit
Plain-language answers about how JobOrbit controls access, handles connected accounts and records activity. We describe only the controls that are in place.
Every person signs in to their own JobOrbit account before they can see any recruitment data.
Owners, managers and recruiters each get access that matches their role in the agency.
Recruiters see the candidates assigned to them. Managers see their assigned recruiters' work.
Tokens for connected accounts, such as Gmail, are stored encrypted rather than in plain text.
Traffic between your browser and JobOrbit is encrypted in transit over HTTPS.
Resumes and documents are served only to signed-in users with access to that candidate — not from public links.
Account owners authorize each connection and can disconnect it at any time.
Recruiters are shown an activity notice, and location sharing can be stopped at any time.
Candidate Gmail and recruiter Gmail are never the same connection. Each is authorized by the person who owns the mailbox.
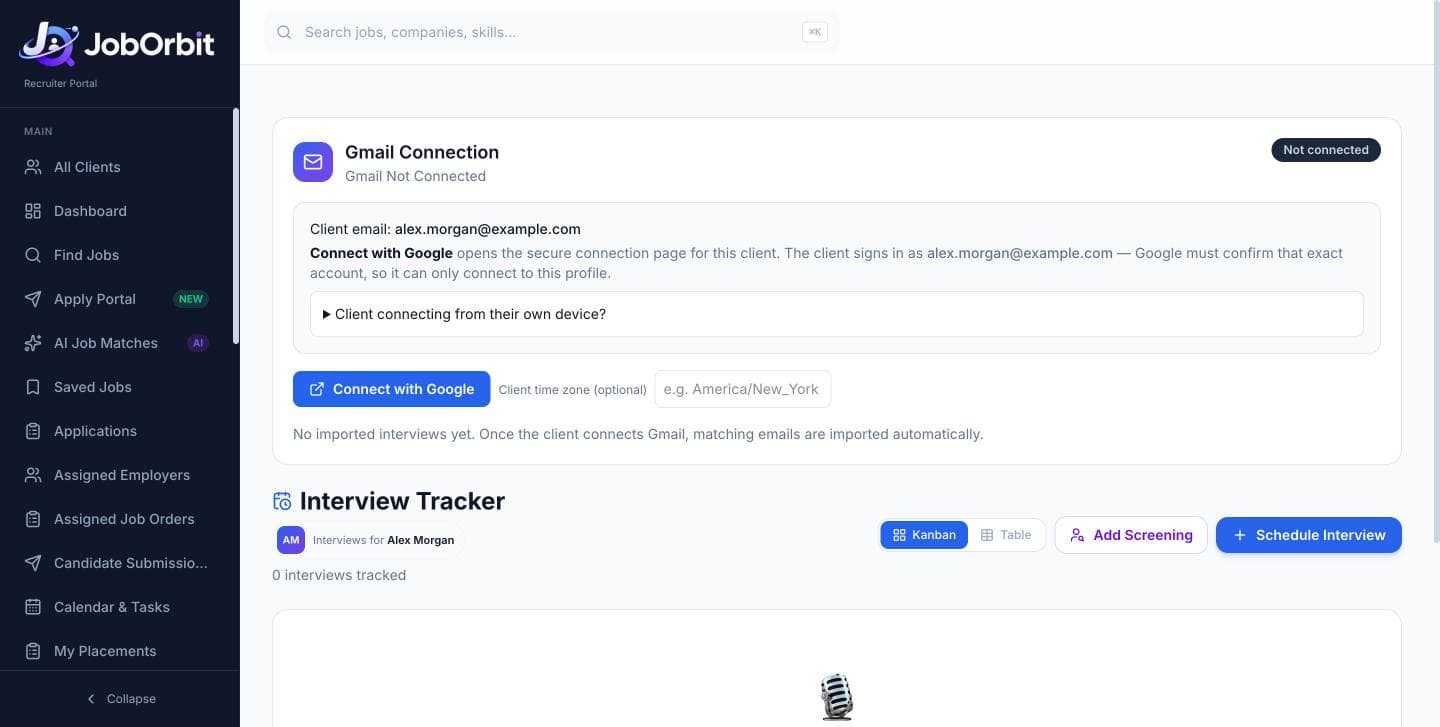
The connection card names the exact email address that must sign in. Google has to confirm that account, so a connection can only attach to the right candidate profile. Until the candidate connects, nothing is imported.
Activity tracking applies only inside the signed-in JobOrbit recruiter workspace, and recruiters are shown a notice explaining it.
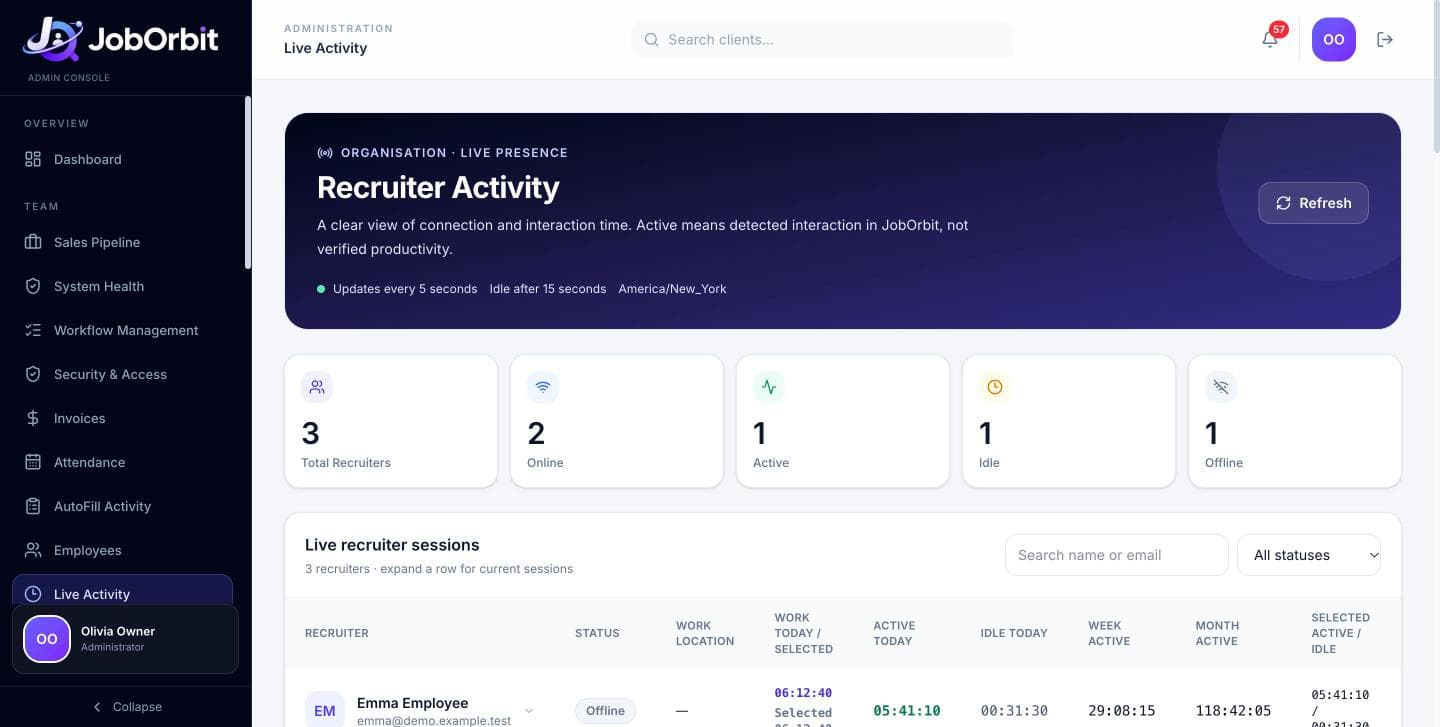
Active means detected interaction, not verified productivity. Location estimates are not proof of physical attendance.
We list only controls that are implemented today and don't claim certifications we haven't earned. If your agency needs a security questionnaire answered, ask us during your demo.
Bring a recruiting workflow to your demo. We’ll walk through it together and discuss pricing for your team.